On-Premise LMS. Deployed Inside Your Network.
Get your on-premise LMS plan.
Talk to our engineers.
On-premise LMS deployment
A learning platform that runs inside your own network
Some organisations cannot put learner data in a vendor's cloud. Regulators forbid it, a data residency clause rules it out, or the security team will not approve an external system holding staff records. We deploy complete learning platforms on infrastructure you control, so training runs without anything leaving your environment.
Deployment targets
- Your own data centre
- Your private cloud tenancy (AWS, Azure, GCP)
- A sovereign or in-country cloud region
- Isolated or air-gapped networks
When on-premise is the requirement, not the preference
Most organisations that ask for this are not making an architectural choice. Something external is forcing it.
Data residency law
GDPR, India's DPDP Act, Saudi PDPL, UAE data protection rules and similar regimes restrict where personal data may be stored and processed. Learner records are personal data.
Contractual obligation
Government, defence and large enterprise contracts often prohibit subcontractor-held data outright, regardless of what the law allows.
Security policy
An internal policy that no third party holds employee records, or a vendor risk process that a SaaS platform cannot pass. Common in financial services and legal.
Isolated networks
Manufacturing plants, remote sites and secure facilities where the platform has to work without reliable internet access, or without any at all.
What gets installed
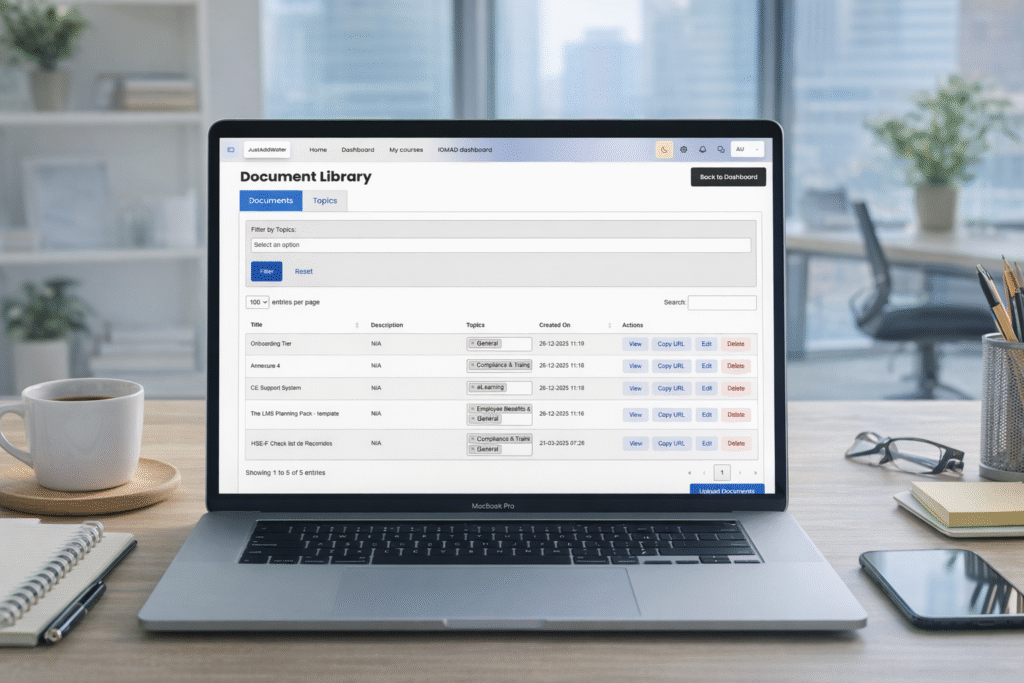
A full learning platform, not a cut-down version. Self-hosted deployment does not mean fewer features, it means the features run on your hardware.
Built on a mature open-source core with our own theme, plugin suite and deployment tooling on top. No licence keys, no phone-home, no external service the platform depends on to function.
Full course and learner management
Course authoring and structure, enrolment rules, cohorts, completion certificates, automated reminders and expiry tracking.
Internal identity integration
Active Directory, LDAP, ADFS, Azure AD or Entra ID, Okta and SAML 2.0, connected over your internal network.
User and role management
Bulk import from your existing records, group and department hierarchy, and role-based curriculum assignment.
Content standards
SCORM 1.2 and 2004, xAPI and AICC. Existing course libraries import without rebuilding, and media is served from your own storage.
Reporting and audit trail
Completion and competency reporting, direct database access for your BI tools, and a change log your auditors can read.
Multi-entity structure
Separate portals per business unit, region or subsidiary, with delegated administration and isolated reporting.
What your infrastructure team provides
The most common reason an on-premise project stalls is an unclear handover between our engineers and the client's IT team. This is the list we send before week one, so that conversation happens early.
Not sure whether your environment fits? Send us what you have and we will tell you plainly whether it works, what needs changing, and what it would cost.
- Server
- A Linux host, or Windows Server with IIS if that is your standard. We have deployed on both. Sizing depends on concurrent learners and whether video is served locally; we specify it during scoping rather than guessing.
- Database
- MySQL or PostgreSQL, either on the same host or on your existing managed database service.
- Storage
- File storage for course content and media. Object storage, NFS or local disk, depending on how your environment is built.
- Network and access
- SSL certificate, DNS entry, and either VPN or bastion access for our engineers during build. Access can be time-limited and revoked at handover.
- Identity
- Service account and endpoint details for your directory, plus whatever approvals your security team requires to issue them.
- Backup
- We configure application and database backups. Where they are stored and how long they are retained is your policy, not ours.
Nothing leaves your environment
The reason most organisations ask for on-premise in the first place. These are the four points a security review tends to test.
No outbound dependency
The platform does not call home, check a licence server, or send telemetry. It runs fully offline if your network requires it.
No vendor-held data
We hold no copy of your learner records. After handover, we have no standing access to the system unless you grant it for support.
Scoped, revocable access
Engineer access during build is named, time-limited and logged. Your team revokes it at go-live and reissues it only when support needs it.
Contractual position
Mutual NDA, full IP assignment to you, and source code delivered at handover. Your security team can review the code they are running.
How a deployment runs
An on-premise build takes the same four weeks as a hosted one, provided infrastructure and access are ready when we start. They usually are not, which is why week one is about your environment rather than ours.
Air-gapped environments add time, because installation and updates move through your approved transfer process rather than over the network. We scope that separately.
Week one
Environment and access
Infrastructure confirmed and provisioned, access approved by your security team, SSL and backups configured, base hardening applied.
Week two
Installation and branding
Platform deployed on your host, theme matched to your brand, course structure and role hierarchy built out.
Week three
Identity and data
Directory connected over your internal network, users imported, existing content and completion history migrated.
Week four
Testing, handover, go-live
Reporting configured, admin training delivered, runbook handed to your IT team, user acceptance testing, then launch.
What your team receives
On-premise only works if the organisation running the server can actually operate it. Handover is a deliverable, not a formality.
- Full source code and database schema
- Deployment and provisioning scripts
- An operations runbook for your infrastructure team: restart, backup, restore, upgrade and log locations
- An administrator guide for your L&D team
- A recorded admin training session
- Integration documentation for each connected system
After go-live
Every deployment includes 60 days of post-launch support. After that, three routes, and all three are genuinely available because you hold the code:
- Retained support with us. Most clients choose this. Defined response times, upgrades and ongoing development.
- Your own IT team. The runbook and documentation are written for this, and we can train your engineers during the build.
- A third party. Standard open-source foundation, documented code, no proprietary lock-in.
Common questions
The questions security teams and infrastructure leads ask before a scoping call.
Schedule a call with our Founder and LMS Expert
Taking Back Ownership: Implementing a Multi-Tenant LMS for a Canadian Pharmacy Network
By taking back ownership of their LMS, the organization reduced recurring costs and gained a flexible foundation for long-term growth.